You can access the distribution details by navigating to My Print Books(POD) > Distribution
Add a Review
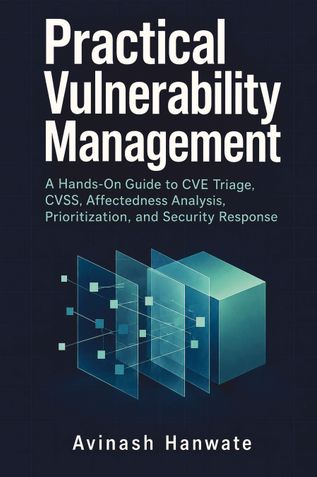
Practical Vulnerability Management
A Hands-On Guide to CVE Triage, CVSS, Affectedness Analysis, Prioritization, and Security Response
Avinash Hanwate
This book ships within India only.
Description
Practical Vulnerability Management is a hands-on guide to understanding, assessing, prioritizing, and responding to software vulnerabilities.
Rather than treating vulnerability management as a scanner-driven exercise, this book focuses on the decisions security professionals make after a vulnerability is discovered: Is the product actually affected? How should the vulnerability be scored? What evidence is sufficient? What should be fixed first? And how can the process be automated without losing human judgment?
The book covers CVE analysis, affectedness assessment, CVSS, prioritization, source-code review, verification, remediation, PSIRT and coordinated disclosure, SBOMs, vulnerability intelligence, and automation.
Practical scenarios and decision exercises help readers apply the concepts to realistic situations involving dependencies, authentication, file boundaries, build configurations, and kernel components.
Designed for cybersecurity practitioners, developers moving into security, vulnerability analysts, Product Security and PSIRT engineers, and anyone responsible for managing software vulnerabilities.
About the Author
Book Details
Publisher: Avinash Hanwate
Number of Pages: 150
Dimensions: 6"x9"
Interior Pages: B&W
Binding:
Paperback (Perfect Binding)
Availability:
In Stock (Print on Demand)
Ratings & Reviews
Practical Vulnerability Management
Review This Book
Write your thoughts about this book.
Currently there are no reviews available for this book.
Be the first one to write a review for the book Practical Vulnerability Management.
Other Books in Computers & Internet
Jacob Francis
PRANAB KUMAR DAS GUPTA

Ankur V. Vyas
MD AZIZUDDIN AAMER