You can access the distribution details by navigating to My Print Books(POD) > Distribution
Add a Review
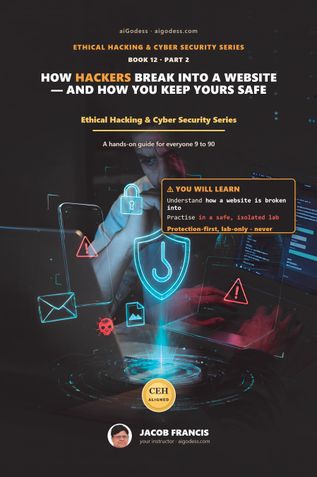
How Hackers Break Into a Website — and How You Keep Yours Safe
Web Servers, Web Apps and the OWASP Top 10 — Spotting and Shutting the Common Web Attacks, the Safe, Lab-Only Way
Jacob FrancisType:
Print Book
Genre: Computers & Internet, Information Technology
Language: English
Price:
₹569
+ shipping
This book ships within India only.
Description
Learn how websites and web apps are attacked, and how to keep your own site safe, in plain words and on your own computer.
Every website is a shop with a counter, a clerk and a storeroom. You type into a login, a search box or a contact form, the clerk carries your words to the storeroom (the database), and a reply comes back. Most break-ins do not smash the window. They quietly trick the clerk. This book shows you how, and how you stop it.
You will follow one press of Enter from your browser to the server and back, read your own site's "shop sign" the way a stranger would, and meet the OWASP Top 10 as ten everyday ways a shop gets tricked: injection, broken access control, misconfiguration, stale software, weak logins and sessions, and more. Each idea starts with a daily-life picture before any technical word.
Then you practise, safely. You open your own practice shop (OWASP Juice Shop or DVWA) bound to your own machine only, and look with real, read-only tools: the browser's developer tools, curl, whatweb, nmap, nikto, and OWASP ZAP and Burp Suite Community. Every command is shown step by step, with a guided practice and a calm reading of what you should see.
You finish able to harden a real site: HTTPS and HSTS, safe input handling, tight permissions, a monthly patch day, security headers, a web firewall, and log watching with a first-hour plan if someone knocks too hard. You will also see how AI now helps both the attacker and the defender.
Protection-first and lab-only: no harmful code and never a live third-party target. Mapped to EC-Council CEH v13 Modules 13 and 14. Book 12 of the Ethical Hacking & Cyber Security Series, written for every reader from 9 to 90.
About the Author
Book Details
Publisher: aigodess.com
Number of Pages: 128
Dimensions: 6.00"x9.00"
Interior Pages: B&W
Binding:
Paperback (Perfect Binding)
Availability:
In Stock (Print on Demand)
Ratings & Reviews
How Hackers Break Into a Website — and How You Keep Yours Safe
Review This Book
Write your thoughts about this book.
Currently there are no reviews available for this book.
Be the first one to write a review for the book How Hackers Break Into a Website — and How You Keep Yours Safe.
Other Books in Computers & Internet, Information Technology
Raut Sarita Somnath, Rohini Sandip Gunjal

G.Jeyakodi
Matthew Morris

Prithwis Mukerjee