You can access the distribution details by navigating to My Print Books(POD) > Distribution
Add a Review
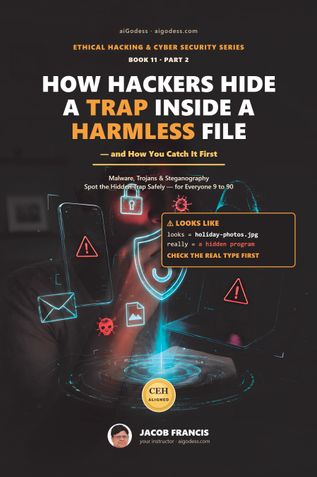
How Hackers Hide a Trap Inside a Harmless File - and How You Catch It First
Malware, Trojans & Steganography - Spot the Hidden Trap Safely, for Everyone 9 to 90
Jacob FrancisType:
Print Book
Genre: Computers & Internet, Information Technology
Language: English
Price:
₹639
+ shipping
This book ships within India only.
Description
Learn to spot malware, Trojans and steganography - the trap hidden inside a harmless-looking file - safely, on your own computer.
A photo from a cousin. An invoice PDF from a courier. A WhatsApp APK that promises a free offer. Each looks like a harmless gift - and each can carry something hidden inside. This book shows you, in plain words and everyday pictures, how that trap is built and how you catch it before you open it.
You will meet the whole malware family - virus, worm, Trojan, ransomware, spyware, adware, rootkit, keylogger and botnet - and learn what each one wants from you. You will see how a double name like invoice.pdf.exe and a borrowed icon fool the eye, and how a secret message can ride inside an ordinary photo or song (steganography).
Then you practise, safely. You build a sealed, offline glass room - a virtual machine on your own computer - and look at files without ever running them: read a file's true type, take its SHA-256 fingerprint, pull out its readable strings, read its hidden details with exiftool, and hide and find a note in your own photo and voice recording with steghide, zsteg and SoX. Every command is real, shown step by step, with a guided practice and a calm reading of what you should see.
You finish with a ten-second check before you open anything, a family plan that makes devices hard to trap and easy to recover with offline backups, and a clear look at how AI now helps both attackers and defenders.
Protection-first and lab-only: no harmful code, only your own machine and your own files. Mapped to EC-Council CEH v13 Module 7 (Malware Threats). Book 11 of the Ethical Hacking & Cyber Security Series - written for every reader from 9 to 90.
About the Author
Book Details
Publisher: aigodess.com
Number of Pages: 176
Dimensions: 6.00"x9.00"
Interior Pages: B&W
Binding:
Paperback (Perfect Binding)
Availability:
In Stock (Print on Demand)
Ratings & Reviews
How Hackers Hide a Trap Inside a Harmless File - and How You Catch It First
Review This Book
Write your thoughts about this book.
Currently there are no reviews available for this book.
Be the first one to write a review for the book How Hackers Hide a Trap Inside a Harmless File - and How You Catch It First.
Other Books in Computers & Internet, Information Technology

Sunil Khandbahale
SIMON GNEZA, CHRIS ABRAMS, JESSICA GNEZA

Parul Saxena, Vinay Saxena, Adarsh Pandey, Uri Flato, ...

प्रेमयोगी वज्र