You can access the distribution details by navigating to My Print Books(POD) > Distribution
Add a Review
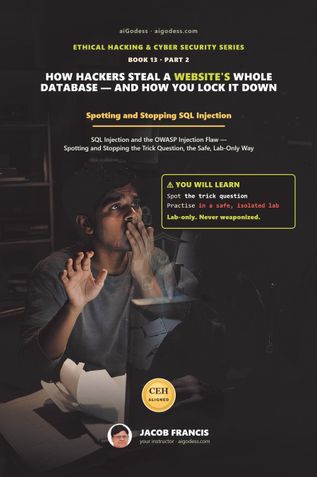
How Hackers Steal a Website's Whole Database — and How You Lock It Down
SQL Injection and the OWASP Injection Flaw — Spotting and Stopping the Trick Question, the Safe, Lab-Only Way
Jacob FrancisType:
Print Book
Genre: Computers & Internet, Information Technology
Language: English
Price:
₹549
+ shipping
This book ships within India only.
Description
Behind every online shop, school portal and booking site sits a storeroom: the database that keeps names, passwords, orders and payments. This book shows you, in plain words, how an attacker can slip that storeroom a trick note through a login box, a search bar or a web address, and make it hand over what it should never show. Then it shows you, step by step, how to lock that door for good.
Written for every reader from 9 to 90, each idea begins with an everyday picture before the technical term. You will learn what SQL is, how a web form asks the database a question, why the classic login trick works, how error messages and blind yes-or-no guessing leak data, and how professionals test with sqlmap, always on your own practice machine and never on anyone else's site.
The real point of the book is defence. You will see how prepared statements (parameterized queries) end the problem at its root, and how input checks with allow-lists, low-privilege database accounts, quiet error pages and a web application firewall add layers behind it. Every chapter closes with a Defence Takeaway, and every command comes with a read-it-like-a-sentence explanation and a Guided Practice on your own lab box.
Mapped to the SQL Injection module of CEH v13 and to the Injection risk in the OWASP Top 10, it suits beginners, parents, small-business owners, students and anyone starting a cyber security career. It ends with a one-page safety sheet, common questions and a glossary. Lab-only, protection-first, and never aimed at anyone else's systems.
About the Author
Book Details
Publisher: aigodess.com
Number of Pages: 113
Dimensions: 6.00"x9.00"
Interior Pages: B&W
Binding:
Paperback (Perfect Binding)
Availability:
In Stock (Print on Demand)
Ratings & Reviews
How Hackers Steal a Website's Whole Database — and How You Lock It Down
Review This Book
Write your thoughts about this book.
Currently there are no reviews available for this book.
Be the first one to write a review for the book How Hackers Steal a Website's Whole Database — and How You Lock It Down.
Other Books in Computers & Internet, Information Technology
Avinash Hanwate
Dr. Ritu Gaurav

Mahesh Athalye

VISHAL SINGH