You can access the distribution details by navigating to My Print Books(POD) > Distribution
Add a Review
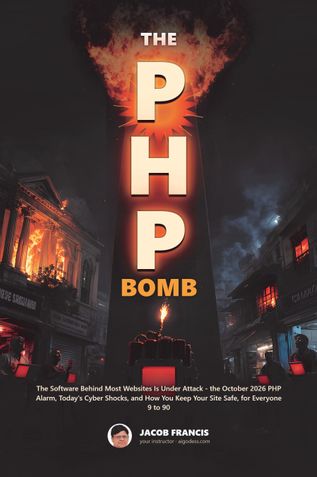
The PHP Bomb
The Software Behind Most Websites Is Under Attack — the October 2026 PHP Alarm, Today's Cyber Shocks, and How You Keep Your Site Safe, for Everyone 9 to 90
Jacob FrancisType:
Print Book
Genre: Computers & Internet, Information Technology
Language: English
Price:
₹579
+ shipping
This book ships within India only.
Description
The quiet engine behind most of the websites you use was in trouble this October. This warm, plain-English book explains what happened, and what you can do about it, whether you are nine or ninety.
Through Maya's small bookshop, young Arun and the retired teacher Mr Thomas, you will meet PHP: the hidden cook in the kitchen behind the web page, the one that prepares each page fresh on millions of shop, school, parish and bank-linked sites. On 21 October 2026 the PHP project released fixed versions of its engine to correct two serious flaws in the engine itself. The book explains in everyday pictures what went wrong inside, why each flaw was scored 9.2 out of 10, and why a severity score is a reason to fix soon, not proof of a break-in.
You will learn why the browser padlock, your password and a normal-looking page cannot tell you whether the engine behind a site is patched. You will see how to read an alarm by its date, its names and its fixed versions, and who must actually apply the fix: your host, your managed provider, or you and the maintainer you hired. A support request you can adapt makes that conversation easy. The book also sets this alarm calmly beside the month's other cyber news, a bank's customer-data notice and warnings about undersea cables and outages, keeping each story in its own lane, each with its own source.
Inside: a step-by-step practice bench on your own computer, real version-check commands in clear four-part blocks, a Defence Takeaway in every chapter, an owner's safety sheet, an incident record, a glossary of words you can understand, and dated sources with a research cutoff.
Protection first, owner-only, never against anyone else's site. A standalone companion in the aiGodess Ethical Hacking & Cyber Security Series.
About the Author
Book Details
Publisher: aigodess.com
Number of Pages: 132
Dimensions: 6.00"x9.00"
Interior Pages: B&W
Binding:
Paperback (Perfect Binding)
Availability:
In Stock (Print on Demand)
Ratings & Reviews
The PHP Bomb
Review This Book
Write your thoughts about this book.
Currently there are no reviews available for this book.
Be the first one to write a review for the book The PHP Bomb.
Other Books in Computers & Internet, Information Technology

DEVANSH ASTHANA

Mr. Ankur Khare, Dr. Ishu Anand Jaiswal, Dr. ...

Jerry Cullen

Chidambaram Jagannathan