You can access the distribution details by navigating to My Print Books(POD) > Distribution
Add a Review
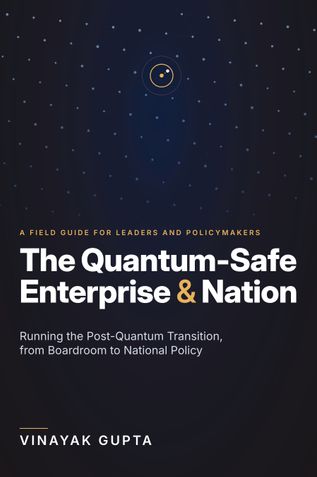
The Quantum-Safe Enterprise & Nation
Running the Post-Quantum Transition, from Boardroom to National Policy
Vinayak Gupta
This book ships within India only.
Description
Quantum computers will break today’s encryption. Data captured today can be decrypted tomorrow. The deadlines are set.
This is the guide for the people who decide: board members, CISOs, regulators and policy advisers. No equations. Just the decisions that matter, in the order they matter.
You will learn how to: test which of your data is already at risk, with one simple inequality (X + Y > Z); build a Cryptographic Bill of Materials before you approve a budget; rank thousands of systems with a transparent, auditable risk score; make the next algorithm change a policy edit, not a rewrite; hold vendors to dated, contractual post-quantum commitments; and coordinate whole sectors, so the weakest link is not the way in.
The book is checked against the NIST standards (FIPS 203, 204 and 205), the NSA’s CNSA 2.0 timeline, U.S. Executive Order 14412, the EU and UK roadmaps, and India’s DST Task Force report on a quantum-safe ecosystem.
It includes a complete enterprise migration playbook, a national policy model for the financial sector, a global deadline map, and a plain-English glossary of every term.
Written by a practitioner for the people who fund, approve and govern the work. The views are the author’s own.
About the Author
Book Details
ISBN: 9789334570281
Publisher: Vinayak Gupta
Number of Pages: 232
Dimensions: 6"x9"
Interior Pages: B&W
Binding:
Paperback (Perfect Binding)
Availability:
In Stock (Print on Demand)
Ratings & Reviews
The Quantum-Safe Enterprise & Nation
Review This Book
Write your thoughts about this book.
Currently there are no reviews available for this book.
Be the first one to write a review for the book The Quantum-Safe Enterprise & Nation.
Other Books in Computers & Internet
José de la Torre Casas


Samir Dash

Matthew Morris